


Top Security Breaches 2026-09-22
Auto-generated 2026-09-22T09:00:32.968703+00:00 (UTC)
-
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
Source: BleepingComputer | Published: 2026-09-19T13:48:32+00:00 | Score: 21.153
The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation’s data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service. […]
-
Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records
Source: The Hacker News | Published: 2026-09-17T07:30:01+00:00 | Score: 18.581
A security breach at Gyazo, Helpfeel’s image-sharing service, exposed about 23.62 million user records, including email addresses and password hashes, the Kyoto-based company said in a notice published Wednesday.
It also exposed about 490 million image metadata records, mostly for images from January 2019 or earlier, including the IDs that make up Gyazo image links.
Helpfeel said
-
Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors
Source: The Hacker News | Published: 2026-09-21T06:06:44+00:00 | Score: 17.604
The North Korean threat actor known as Jade Sleet has been attributed to the compromise of an India-based “much smaller organization” in the information technology (IT) services industry, once again highlighting how the adversary continues to target developers to breach target networks.
Cybersecurity company SentinelOne, which disclosed details of the activity, said it involved the use of Apple
-
BigCommerce alerts merchants of data breach linked to Ribon apps
Source: BleepingComputer | Published: 2026-09-21T21:18:49+00:00 | Score: 17.45
Ecommerce platform BigCommerce has alerted multiple merchants to data breaches after attackers compromised credentials for third-party Ribon applications and used them to inject malicious scripts into online stores. […]
-
Threat Intelligence Alone Won’t Close the Exploitation Gap
Source: The Hacker News | Published: 2026-09-16T11:15:48+00:00 | Score: 16.528
A leaked credential shows up in a criminal marketplace, or a vulnerability gets a disclosure advisory, and either one can be weaponized against a real target before most security teams have triaged the alert. Attackers are combining that kind of intelligence with AI-assisted exploitation to accelerate the path from exposure to breach faster than most security programs are built to react.
-
Identity Visibility in 2026: The Foundation of Identity Security
Source: The Hacker News | Published: 2026-09-19T13:28:41+00:00 | Score: 15.656
Identity visibility is a starting point for modern identity security, because stolen and misused credentials are among the most frequently reported initial access vectors in breach research, including Verizon’s annual Data Breach Investigations Report. This article explains what identity visibility means in IAM, why cloud and multicloud environments complicate it, which capabilities matter in
-
TASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard Data
Source: The Hacker News | Published: 2026-09-21T14:15:40+00:00 | Score: 14.106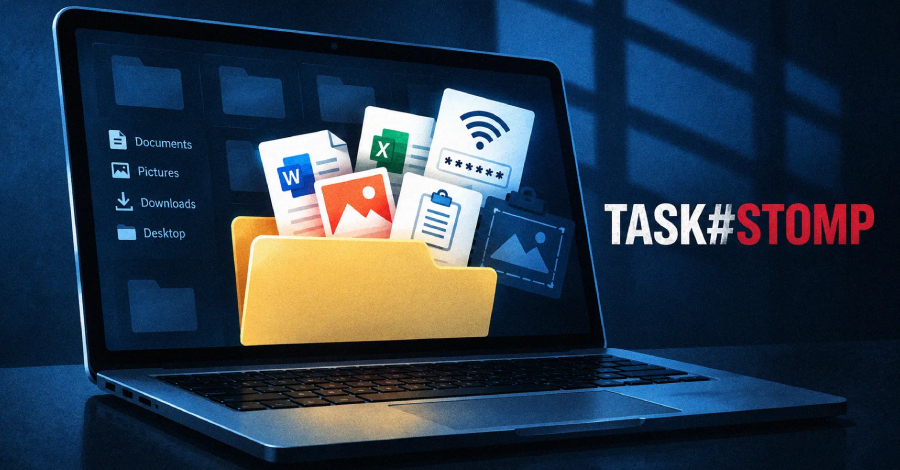
Cybersecurity researchers have disclosed details of a new campaign dubbed TASK#STOMP that delivers a PowerShell backdoor designed to harvest sensitive data from compromised hosts.
The backdoor “automatically harvests and exfiltrates business documents, watches the filesystem for new files in real time, steals Wi-Fi passwords and clipboard contents, takes screenshots, and accepts arbitrary
-
CISO’s Expert Guide to Agentic Pentesting for Websites
Source: The Hacker News | Published: 2026-09-17T10:50:53+00:00 | Score: 13.223
Attackers now weaponize new vulnerabilities in about five days (Mandiant, part of Google Cloud). The median organization takes 43 days to patch one (Verizon DBIR 2026). A new free guide explains how autonomous AI agents are closing that gap, and what security leaders must demand before pointing one at production.
TL;DR
Exploitation is now the front door. It starts 31% of breaches (Verizon DBIR
End of report.
