

Top Security Breaches 2026-09-29
Auto-generated 2026-09-29T09:00:44.133957+00:00 (UTC)
-
ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants
Source: The Hacker News | Published: 2026-09-23T05:30:09+00:00 | Score: 17.896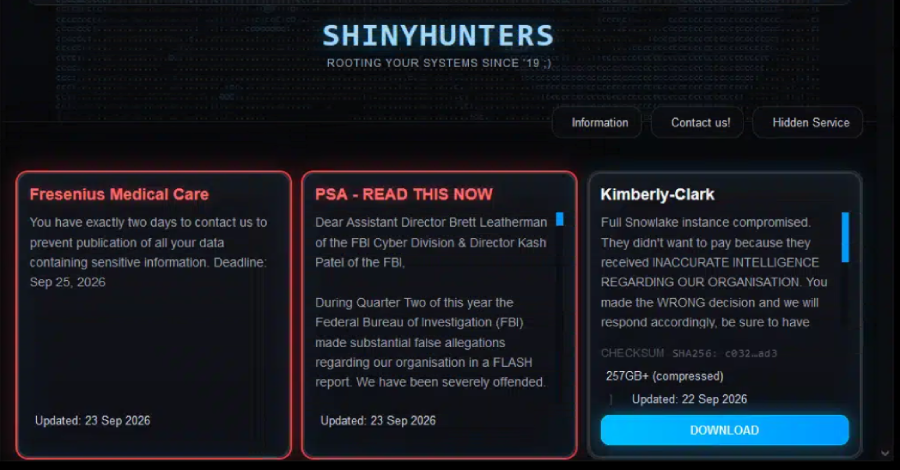
The cyber extortion group known as ShinyHunters on Tuesday claimed it had breached the U.S. Federal Bureau of Investigation and stolen data belonging to current and former employees at the agency.
“We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job,” the group said in a statement posted on their dark
-
Times Car confirms data breach affecting 6.6 million user accounts
Source: BleepingComputer | Published: 2026-09-28T20:31:16+00:00 | Score: 17.141
Japanese car-sharing service Times Car has confirmed that approximately 6.6 million user accounts were compromised in a cyberattack disclosed late last week. […]
-
Carbonato Botnet Compromises Docker Hosts to Deploy Telegram-Controlled Hermes AI Agent
Source: The Hacker News | Published: 2026-09-28T11:46:00+00:00 | Score: 15.875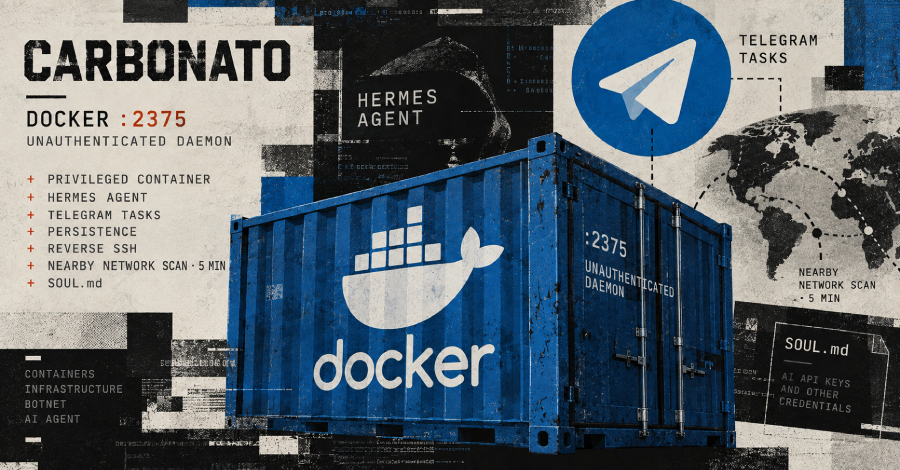
Cybersecurity researchers have disclosed details of a new botnet malware called Carbonato that’s targeting exposed Docker daemons to deploy an open-source artificial intelligence (AI) agent framework called Hermes Agent.
“The implant installs the framework unchanged, then overwrites its SOUL.md persona file,” ThreatDown said. “The 39-line prompt directs it to execute tasks received through
-
Secrets Sprawl Is an Identity Problem That AI Just Made Impossible to Ignore
Source: The Hacker News | Published: 2026-09-24T11:00:00+00:00 | Score: 15.025
AI coding agents are changing how quickly developers can build and ship software as well as how quickly credentials can become exposed. According to GitGuardian’s 2026 State of Secrets Sprawl Report, commits identified as AI-assisted are leaking secrets at approximately twice the rate of human-written ones. Most of the fastest-growing categories of leaked credentials are now connected to AI
-
Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks
Source: The Hacker News | Published: 2026-09-28T18:35:42+00:00 | Score: 14.52
Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis.
The malware has been seen in a small number of targeted intrusions at telecommunications organizations, universities, medical nonprofits, intergovernmental organizations, and government contractors. Its use goes back to at least
-
⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats
Source: The Hacker News | Published: 2026-09-28T14:00:53+00:00 | Score: 12.663
A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into live attack surface.
Elsewhere, weak service accounts, old bugs, exposed systems, phishing kits, and strangely easy exploit paths kept doing useful work for attackers. Nothing
-
Bitget resumes Bitcoin withdrawals after $387.5 million crypto heist
Source: BleepingComputer | Published: 2026-09-28T09:25:29+00:00 | Score: 12.538
Cryptocurrency exchange Bitget has resumed Bitcoin withdrawals suspended after suspected North Korean hackers breached its systems last week and stole over $350 million. […]
-
JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources
Source: The Hacker News | Published: 2026-09-28T09:08:21+00:00 | Score: 12.242
The threat actor known as JADEPUFFER has been observed orchestrating destructive actions within a Microsoft Azure environment using compromised service principals.
Microsoft, which is tracking the activity under the name Storm-3168, has called it an evolution of the threat actor’s tradecraft. The attack took place in early June 2026 over a period of about 18 hours.
“The destructive operations
End of report.
