

Top Security Breaches 2026-10-13
Auto-generated 2026-10-13T09:00:40.563812+00:00 (UTC)
-
Attackers Hijack .gh, .sl, and .as Registries to Obtain Certificates for Google Domains
Source: The Hacker News | Published: 2026-10-07T18:48:17+00:00 | Score: 16.263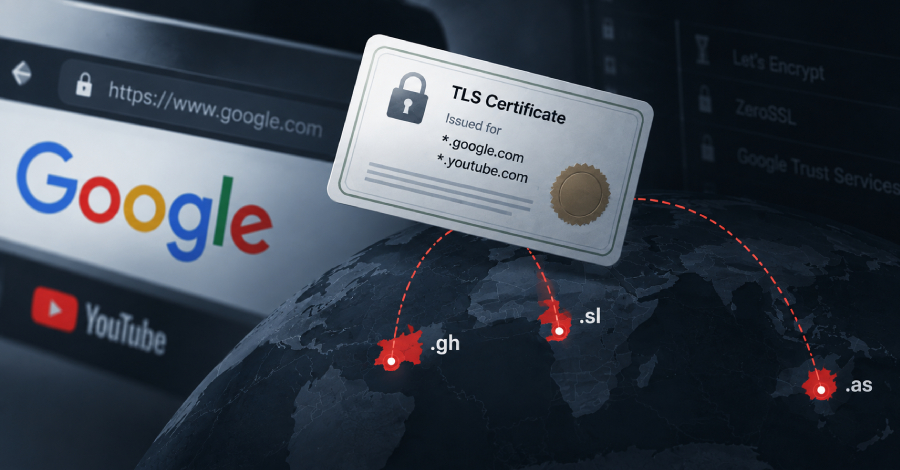
Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6.
Google’s own systems were not breached, but any domain ending in .gh (Ghana), .sl (Sierra Leone) or .as (American Samoa) was put at risk. With such a certificate, an attacker could pose as the real site over an encrypted
-
ThreatsDay: Ransomware Affiliate Betrayal, WhatsApp RAT, Exposed Hacker Tools and 12 More Stories
Source: The Hacker News | Published: 2026-10-08T17:58:02+00:00 | Score: 16.012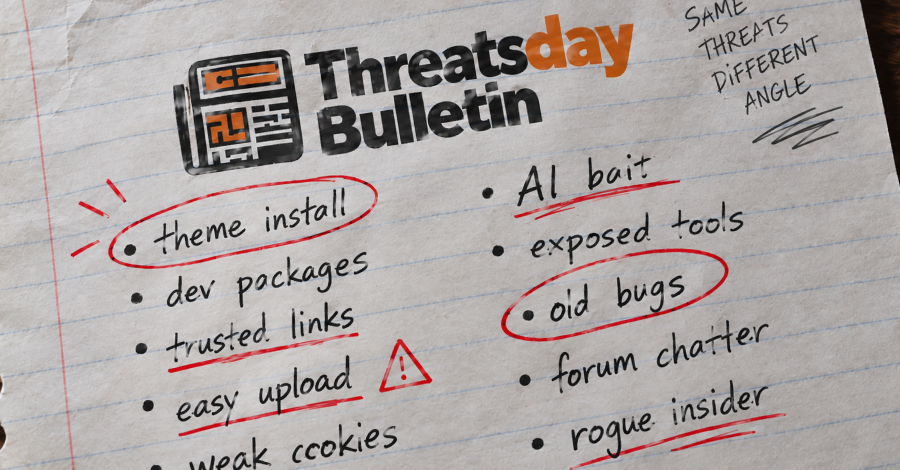
The crooks have trust problems of their own. One ransomware affiliate decided to keep the profits for himself. Elsewhere, an attacker left a server exposed, complete with tools and traces of an intrusion. Apparently, keeping things secure is a problem on both sides of the fence.
The rest of the week isn’t much more reassuring. Malicious code turned up in developer packages and extensions that
-
FBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jobs Portal Hack
Source: The Hacker News | Published: 2026-10-09T17:45:26+00:00 | Score: 15.409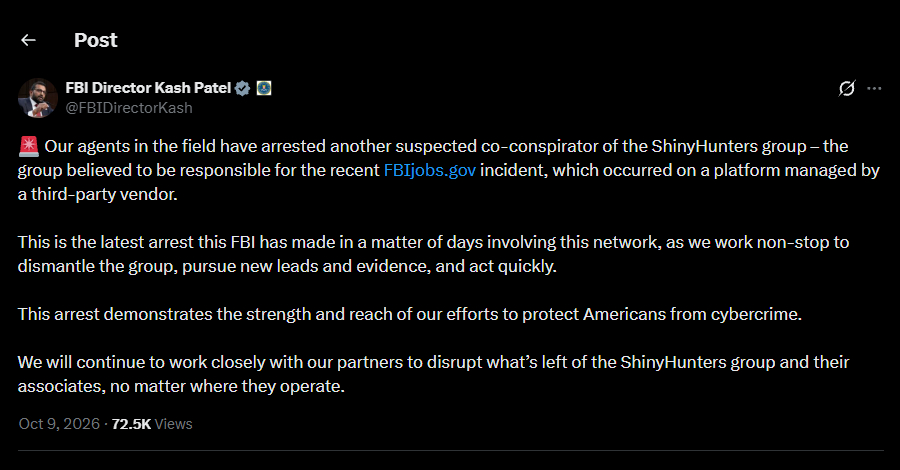
The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X.
ShinyHunters is the extortion group that said in September it had breached the FBI’s jobs portal and stolen sensitive data on almost all FBI agents and job applicants. The FBI has not named the suspect, and no charges have been made public.
The
-
MonsterCloud Owner Accused of Billing Over $19M While Secretly Paying Ransoms to Decrypt Data
Source: The Hacker News | Published: 2026-10-08T07:41:44+00:00 | Score: 14.084
The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying the attackers to obtain decryptors while claiming to use proprietary tools to recover their data.
Zohar Pinhasi (aka Zack Silver and Zack Green) has been charged with two counts of wire fraud and one count of wire
-
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More
Source: The Hacker News | Published: 2026-10-12T15:16:26+00:00 | Score: 13.578
Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That’s not much time to read the warning, let alone do something about it.
But speed is only part of the problem. A secure connection didn’t always mean a safe destination. People offering to fix a ransomware mess had questions to answer themselves.
-
Japan Sees Sharp Rise in Web Data Leaks Amid Mobile API Abuse and Metabase Attacks
Source: The Hacker News | Published: 2026-10-08T15:45:56+00:00 | Score: 13.285
Attackers behind a string of personal data leaks at Japanese organizations have abused APIs for mobile apps and targeted known software flaws, the JPCERT Coordination Center (JPCERT/CC) said.
The Tokyo-based center, which takes incident reports, based its October 8, 2026 alert on those reports and other information. The alert names no attacker and no affected organization.
JPCERT/
-
Anthropic takes risky AI tests offline after models breach govt sites
Source: BleepingComputer | Published: 2026-10-12T18:51:59+00:00 | Score: 12.943
Anthropic announced that its internal AI models undergoing “high-risk and cybersecurity evaluations” no longer have internet access following incidents involving U.S. government websites at the federal, state, and local levels. […]
-
Saudi Arabia further suspends flights after latest deadly Houthi attack on airport
Source: World news | The Guardian | Published: 2026-10-12T15:42:37+00:00 | Score: 12.12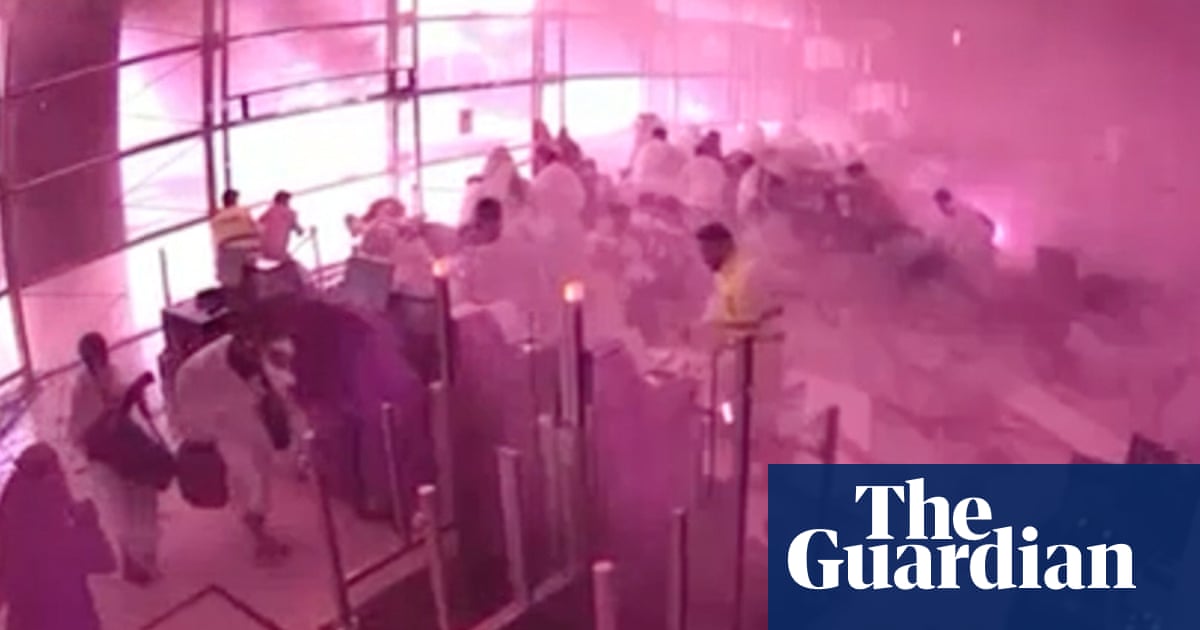
Energy minister says ‘fear has no place in the Saudi lexicon’ as paramilitary group again breaches stretched defences Why are the Houthis attacking Saudi airports and how are the missiles getting through? Saudi Arabia has been forced to suspend all flights to and from its main international airport in Riyadh until next Saturday after a further round of Houthi missile attacks caused more damage and left one person dead. Some airlines, including Gulf Air and Bahrain Air, had already said they were cancelling flights until next Saturday. More missiles were fired at Saudi Arabian cities by the Houthis on Monday, Saudi Arabian’s military spokesperson said. The Gulf nation announced it was suspending flights from Riyadh, its second busiest airport, after Houthi missiles killed 13 people on Saturday and left more than 300 injured. Saudi state TV broadcast CCTV footage that showed passengers deluged in smoke and falling masonry as they queued at the airport terminal to board a plane just as the Houthi missile struck. Continue reading…
End of report.
