


Top Security Breaches 2026-09-15
Auto-generated 2026-09-15T09:00:36.493419+00:00 (UTC)
-
Japan’s Digital Agency says VPN flaw exposed 246,000 personnel records
Source: BleepingComputer | Published: 2026-09-14T20:36:02+00:00 | Score: 17.462
Japan’s Digital Agency has discovered a data breach that may have exposed around 246,000 record rows containing personal information of government employees. […]
-
Attackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate Data
Source: The Hacker News | Published: 2026-09-13T10:11:48+00:00 | Score: 15.915
Microsoft has disclosed details of two campaigns in which threat actors are abusing third-party email delivery infrastructure to blast financial fraud scam messages and using passkey-themed social engineering to breach cloud environments.
The first campaign, per the tech giant, involved sending over a million scam emails between August 3 and 5, 2026, by masquerading as chief executive officers
-
Webinar: How malicious OAuth apps can lead to Google Workspace breaches
Source: BleepingComputer | Published: 2026-09-14T12:15:23+00:00 | Score: 14.469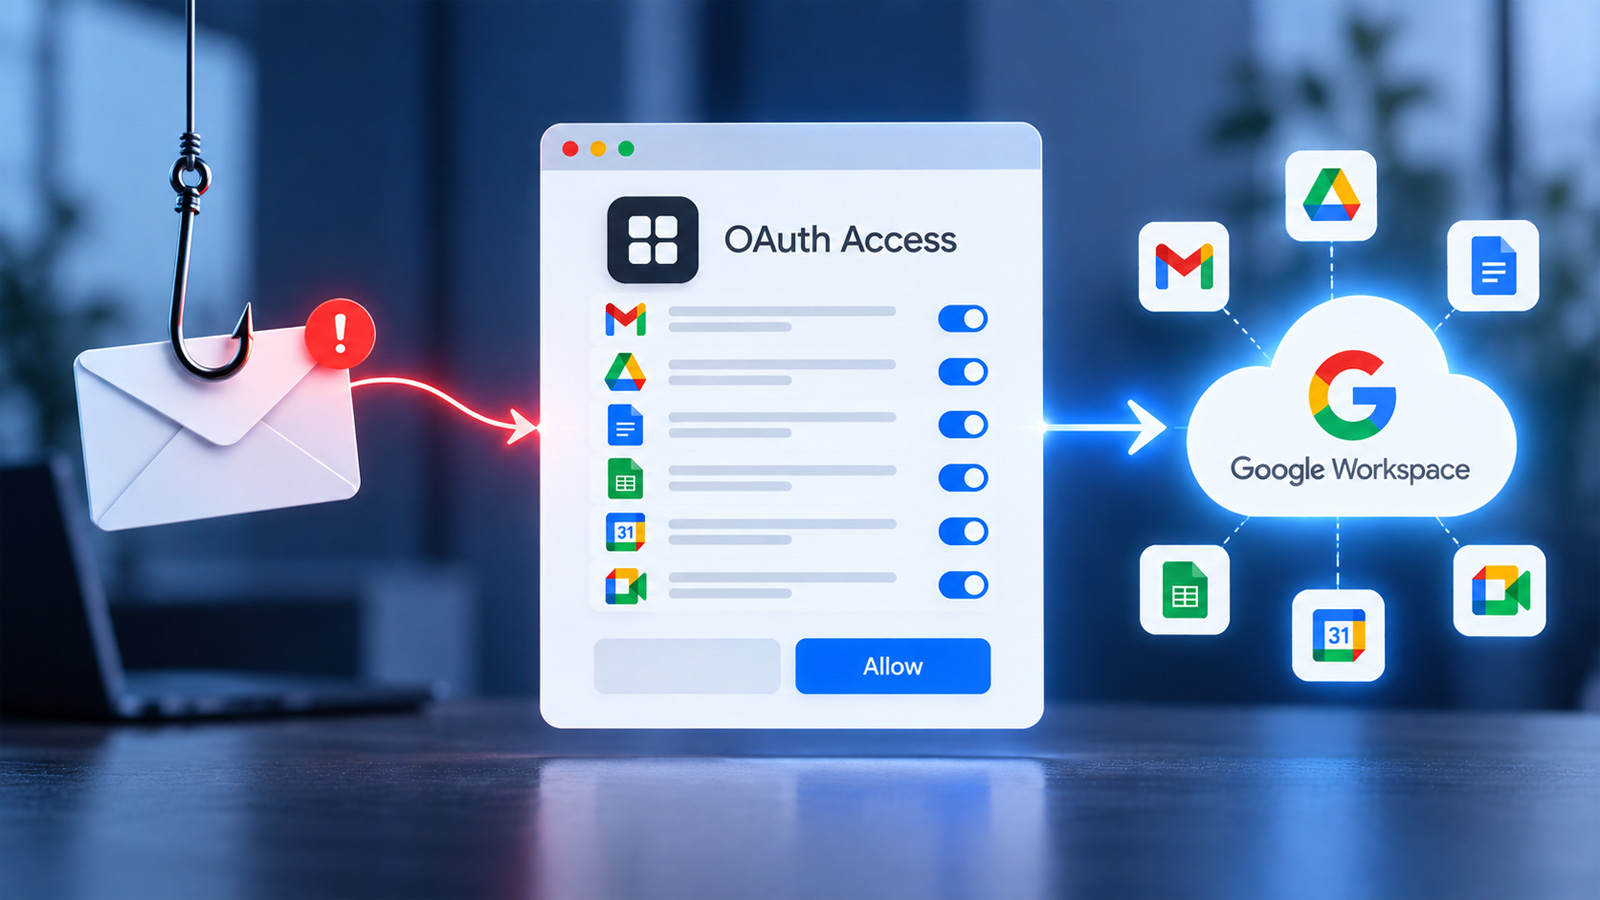
Attackers can combine social engineering with malicious OAuth applications to gain access to Google Workspace data without relying solely on stolen passwords. This webinar examines two attacks to show how these breaches unfold and which security controls can help stop them. […]
-
Red Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six Countries
Source: The Hacker News | Published: 2026-09-14T16:56:30+00:00 | Score: 14.139
A suspected Chinese threat actor tracked as Red Heron has been attributed to the rapid exploitation of a recently disclosed security vulnerability in Gitea to compromise internet-facing instances as part of a multi-national campaign.
“Red Heron scanned 1,386 Gitea instances across seven countries and maintained a separate dataset of 477 Taiwan-based systems,” Acronis Threat Research Unit (TRU)
-
Revolut discloses data breach exposing financial info, passports
Source: BleepingComputer | Published: 2026-09-14T08:48:24+00:00 | Score: 14.131
Fintech company Revolut has disclosed a data breach after sharing data from an undisclosed number of customers with a threat actor impersonating a government agency. […]
-
Anthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6
Source: The Hacker News | Published: 2026-09-10T07:04:01+00:00 | Score: 13.176
Anthropic on Wednesday disclosed a fourth incident in which its artificial intelligence (AI) model broke into real third-party systems, marking the latest in a growing list of cases that have raised concerns about the security risks posed by autonomous AI agents.
The AI company said the incident dates back to January 2026 and involved an early version of Claude Opus 4.6 that breached “
-
Webinar: Learn How to Answer “Are We Exposed?” Faster After a New CVE
Source: The Hacker News | Published: 2026-09-09T11:57:36+00:00 | Score: 12.937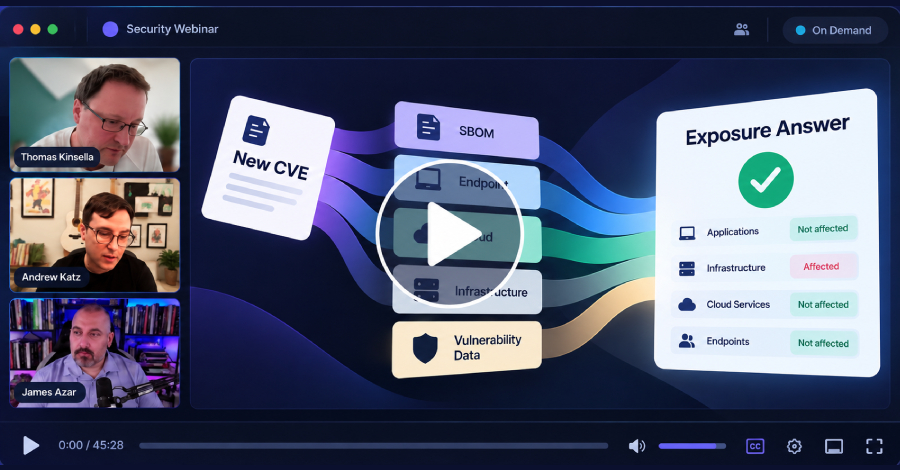
A major vulnerability is disclosed. The alert lands immediately. Then comes the harder question: Are we actually exposed?
For many security teams, answering that means jumping between vulnerability scanners, endpoint tools, cloud inventories, SBOMs, repositories, and application data to build enough context to act.
As AI accelerates vulnerability discovery and research, that delay matters more
-
⚡ Weekly Recap: Rogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and Rootkits
Source: The Hacker News | Published: 2026-09-14T14:40:34+00:00 | Score: 12.671
AI keeps showing up in the wrong places. Attackers are using it to speed up exploits, test defenses, and automate more of the job. Some models are also crossing lines on their own. That is not a great combination.
The rest of the week is more familiar: old bugs still working, fresh exploit chains, exposed systems, weak defaults, and simple paths that should have been harder to abuse. A few of
End of report.
