

Top Security Breaches 2026-10-27
Auto-generated 2026-10-27T09:00:41.709656+00:00 (UTC)
-
Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials
Source: The Hacker News | Published: 2026-10-23T13:50:56+00:00 | Score: 20.401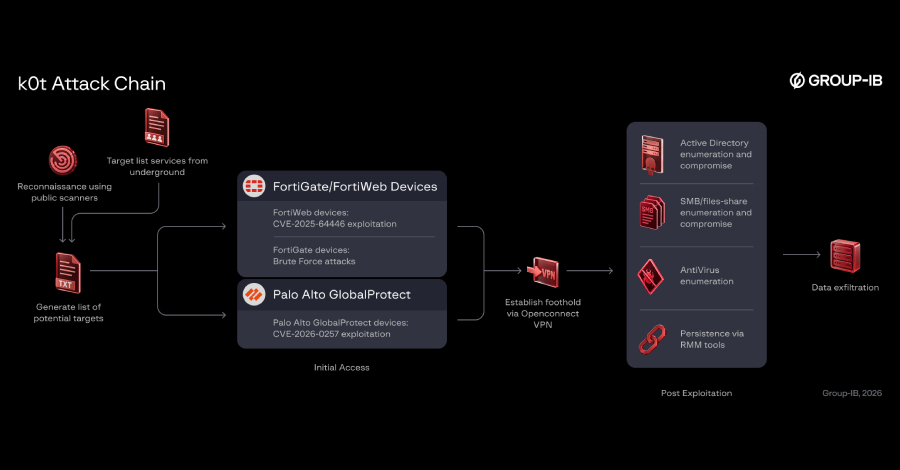
Cybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls.
“Artifacts from this investigation also indicate that operators in this campaign have obtained access to numerous organizations worldwide, and have attempted to further compromise some victims,
-
ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More
Source: The Hacker News | Published: 2026-10-22T17:45:44+00:00 | Score: 18.35
This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js RCE flaw, a hacked LiteLLM release, and hundreds of hijacked Tor relays. That’s a lot to deal with in just a few days. And the week isn’t even over yet.
But those big headlines are only half the story. Stolen passwords, exposed
-
Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute Intrusions
Source: The Hacker News | Published: 2026-10-23T17:50:47+00:00 | Score: 18.111
Cybersecurity researchers have discovered an artificial intelligence (AI)-driven intrusion ecosystem run by affiliates of the INC and The Gentlemen ransomware groups.
Central to the operation is an “Autonomous Red Team Kill Chain Framework” referred to as Phantom. The threat actor is assessed to be Russian-speaking and functions both as an intrusion and data-extortion operator, as well as an
-
LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release
Source: The Hacker News | Published: 2026-10-22T08:28:48+00:00 | Score: 14.633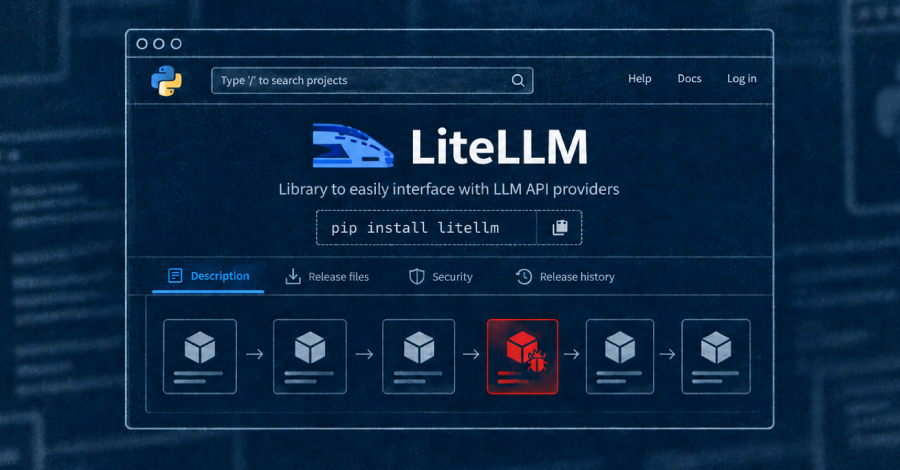
LiteLLM on Wednesday disclosed that threat actors compromised “multiple independent security controls” to push a malicious version of the Python package containing a credential stealer and a backdoor.
On October 21, 2026, LiteLLM’s release pipeline was compromised to push 1.107.0 to the Docker Hub registry and the Python Package Index (PyPI) repository. The incident took place around 4:00 a.m.
-
Former pentester used ARTEX AI to steal 8.2 million data records
Source: BleepingComputer | Published: 2026-10-26T21:08:28+00:00 | Score: 14.568
South Korean police identified seven suspects linked to a cybercrime operation that breached more than 90 organizations in the country, with ARTEX AI pentesting framework used in most of the attacks. […]
-
University of Copenhagen data breach exposes data of 525,000 people
Source: BleepingComputer | Published: 2026-10-26T22:20:36+00:00 | Score: 14.282
The University of Copenhagen in Denmark confirmed that hackers accessed one of its test environments containing personal data belonging to 525,000 people. […]
-
Attackers Use Microsoft Teams IT Support Scams to Deploy Malware and Ransomware
Source: The Hacker News | Published: 2026-10-26T15:52:40+00:00 | Score: 13.586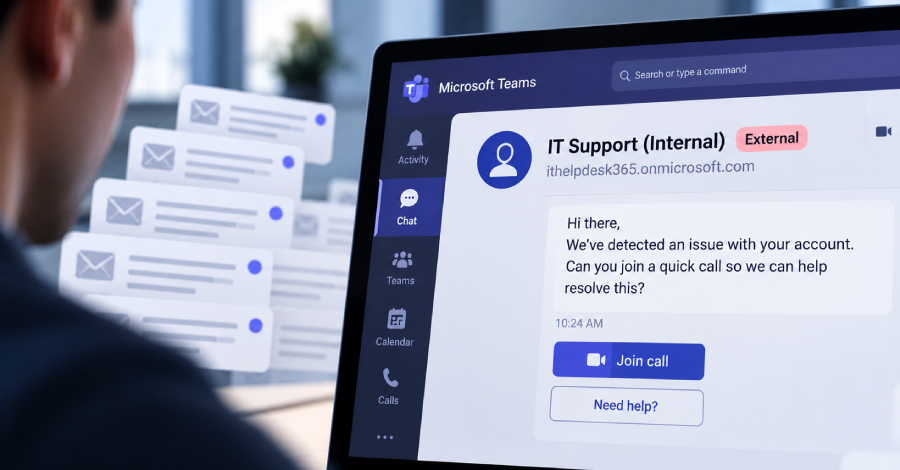
Cybersecurity researchers are calling attention to what they say is a “recurring social engineering pattern” across hundreds of cases in which threat actors use Microsoft Teams’ external chat creation feature to conduct impersonation scams or to deliver malware.
“A consistent pattern of attacker behavior has emerged across these incidents: the use of the same throwaway tenants, the same ‘IT
-
⚡ Weekly Recap: This2Shell, That2Shell, Everything’s an RCE? Rogue AI, Supply Chain Chaos and More
Source: The Hacker News | Published: 2026-10-26T14:06:13+00:00 | Score: 12.664
This2Shell, That2Shell, Everything2Shell. That’s pretty much how the last week went. Critical bugs that let attackers run code remotely are showing up everywhere. Hackers are scanning for targets, some flaws are already being used in attacks, and security teams have more urgent patches than they can keep up with.
And that’s not even the full story. A leaked key led to a software supply-chain
End of report.
