

Top Security Breaches 2026-11-17
Auto-generated 2026-11-17T09:00:37.298075+00:00 (UTC)
-
Cursor Says Stolen Fireworks AI Key Led to Trojanized Claude Code Extension Incident
Source: The Hacker News | Published: 2026-11-15T08:22:04+00:00 | Score: 22.732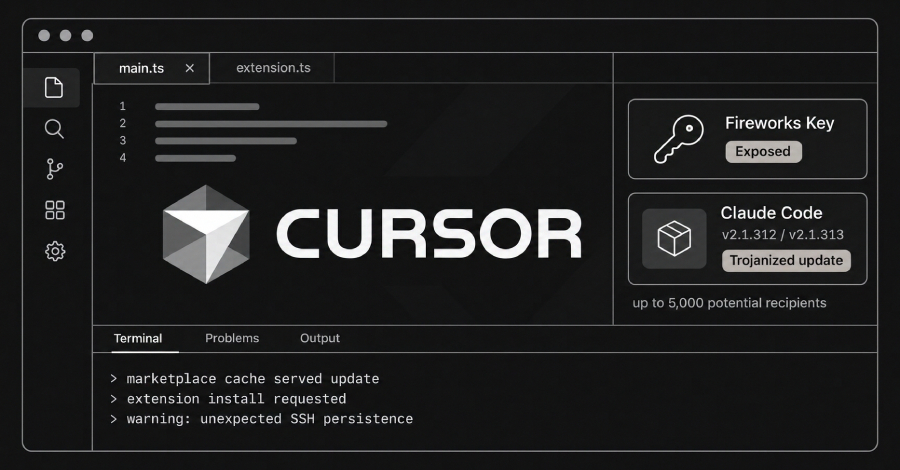
The compromise of Anthropic’s official Claude Code extension on Cursor’s extension marketplace was the result of the theft of an access key that was exposed in the wake of a breach targeting Fireworks AI.
“An attacker obtained an access key we had issued to Fireworks,” Cursor said in a Friday update. “The key was exposed by Fireworks, and the attacker used it to copy data from a read-only
-
Fandango says hackers stole payment card details from checkout pages
Source: BleepingComputer | Published: 2026-11-16T15:44:21+00:00 | Score: 17.408
Ticket seller Fandango Media is notifying customers about a data breach that exposed payment card details entered on its checkout pages. […]
-
Over 35,000 Grok-Built Apps Exposed Online, Some Leaking Confidential Data and Passwords
Source: The Hacker News | Published: 2026-11-11T12:19:40+00:00 | Score: 16.542
Of the 37,571 Grok-built apps that security company Claroc found online, 35,578 were open to anyone without a sign-in, the researchers said yesterday.
They included 24 apps built by staff at the social network X and at SpaceXSI, the company that makes the Grok AI assistant. Most of the open apps were games, landing pages, and calculators, but about 1 in 10 contained internal business or
-
Railway Says Stolen Customer AI Keys Led to $740,000 in Estimated Unauthorized Usage Charges
Source: The Hacker News | Published: 2026-11-11T07:49:04+00:00 | Score: 14.685
AI provider keys that customers stored on Railway were stolen in an October breach and used to commit an estimated $740,000 in unauthorized spending, the platform-as-a-service provider said yesterday. It has promised to pay those charges itself when an AI provider will not refund them.
The company builds and runs apps for its customers and stores their secrets, such as API keys and database
-
SGLang RCE Exploit Breaches NEAR AI, Steals Data From 18 Agents and About 100 Users
Source: The Hacker News | Published: 2026-11-10T19:19:39+00:00 | Score: 14.529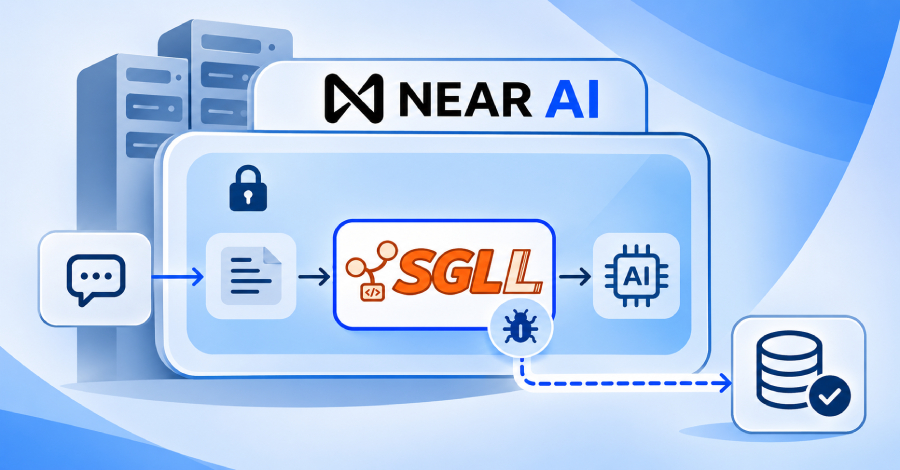
An attacker exploited a remote code execution flaw in SGLang, an open-source inference engine, and ran code on one of NEAR AI’s inference servers last Sunday.
The attacker could also have seen requests being processed on that server that day, including requests sent in confidential mode, the company said earlier this week. That mode processes requests inside a trusted execution environment (TEE
-
Uber notifies drivers of data breach affecting nearly 150,000 people
Source: BleepingComputer | Published: 2026-11-17T08:35:42+00:00 | Score: 14.395
Ride-hailing company Uber is notifying nearly 150,000 drivers that attackers stole their data after breaching AI infrastructure provider Fireworks in early October. […]
-
Google Cloud Warns Three AMD Turin CPU Flaws Could Leak Data Across Processes in VMs
Source: The Hacker News | Published: 2026-11-12T12:09:14+00:00 | Score: 13.239
Google Cloud VMs on AMD Turin chips need a guest OS patch and a stop-and-start to protect against three CPU side-channel flaws, Google said this week.
The company has already applied mitigations against attacks between VMs, and between VMs and the host. Inside a VM, the flaws may let an attacker with code on the same processor core infer data from other processes or the kernel.
The affected
-
Node.js Fixes 16 Flaws, Including HTTP/2 Bugs That Crash Servers and Leak Other Connections’ Data
Source: The Hacker News | Published: 2026-11-12T08:20:37+00:00 | Score: 13.192
A flaw fixed in Node.js this week lets unauthenticated clients crash servers that use the runtime’s built-in HTTP/2 support on the 24.x and 26.x release lines. A second HTTP/2 flaw can cause a server to send a client pieces of its memory, including responses intended for other connections.
Fixed versions were released for all three supported lines: 22.23.5, 24.22.3, and 26.13.1.
The crash
End of report.
